AI security ·
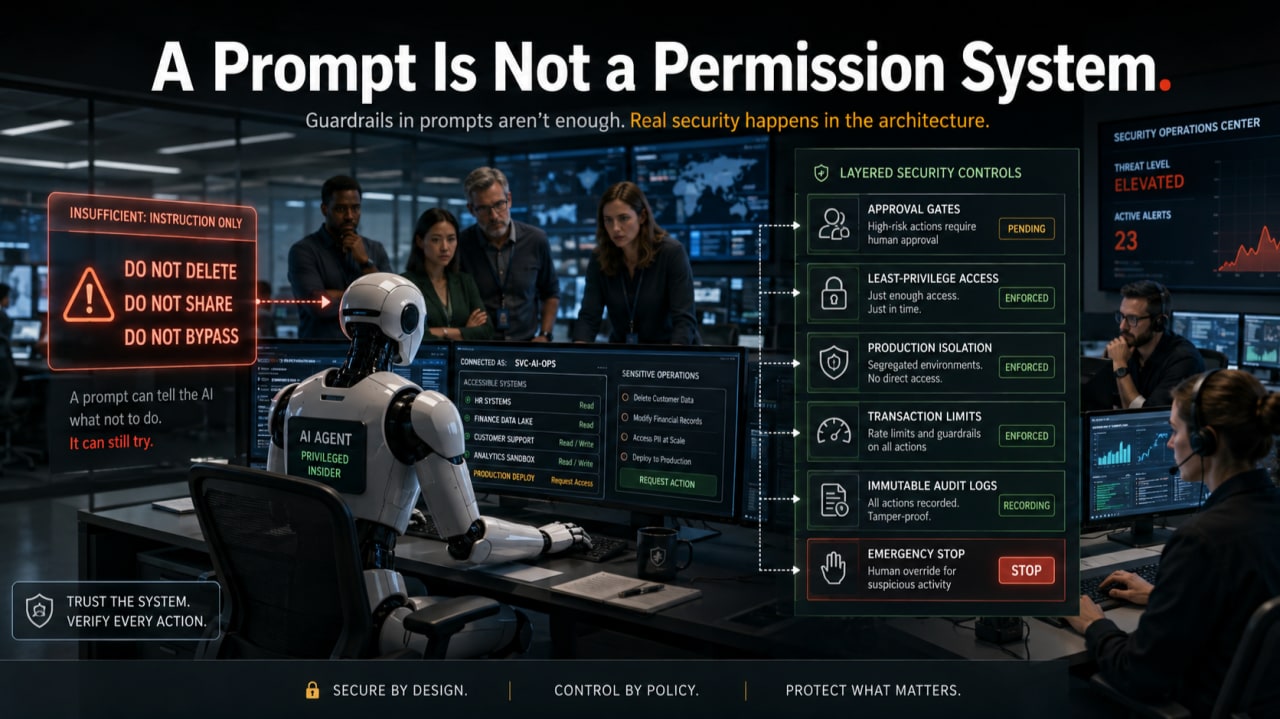
🔐 Your AI Guardrail Is Not a Security Control
Why instructions inside a prompt cannot restrain an overprivileged AI agent, and why security must be enforced through permissions, approvals, separation, logging, limits, and kill switches.
The central idea
An AI agent's guardrail is not a security boundary. Organizations must assume an agent may make the wrong decision and use technical controls to prevent or contain harmful actions.
What leaders should take away
- Give agents only the permissions they need and isolate test activity from production systems.
- Require human approval for destructive actions involving money, sensitive data, identities, or infrastructure.
- Log consequential actions, set enforceable limits, and maintain a tested kill switch for high-risk workflows.
Why this matters
AI changes the speed and scale at which organizations can act. That makes operating clarity, trustworthy information, and accountable human judgment more important—not less. The practical goal is to connect new capability to work that matters while making the boundaries visible.
Questions to ask next
- What business outcome are we trying to change?
- Who owns the information, decision, and resulting action?
- What evidence would show that this approach is working?